Understanding Active Directory: The Technology Behind Enterprise AI Security - Part 1: Understanding the Basic Concepts
Understanding the account infrastructure behind AI systems
When planning an internal AI system, you may need to connect questions such as who can use it and which information they can access to the organization’s account management. Active Directory is one of the foundations worth understanding.
This series focuses on Active Directory Domain Services (AD DS) in Windows Server, covering accounts, authentication, permissions, and operations. Before considering how to connect an AI application, let’s understand what the underlying infrastructure does.
Part 1 covers the information AD DS manages, its relationship with DNS, and the differences between Kerberos, NTLM, and Basic authentication. The comics use fictional conversations to explain concepts; primary sources for the technical explanations appear at the end of each section.
Series Outline
- [★This installment★] Chapter 1: Understanding the basics - Fundamentals of Active Directory and Kerberos/NTLM authentication
- Chapter 2: Building a domain environment - Setting up a lab environment
- Chapter 3: Joining clients and servers to the domain - Domain join in detail
- Chapter 4: Proxy servers and Integrated Windows Authentication
- Chapter 5: Browser configuration and authentication - Settings for each browser
- Chapter 6: Troubleshooting - Common problems and solutions
- Chapter 7: Security and best practices - Considerations for production environments
- Chapter 8: Practical configuration examples - Integration with AI security tools
1.1 Active Directory fundamentals
1.1.1 The role and functions of AD
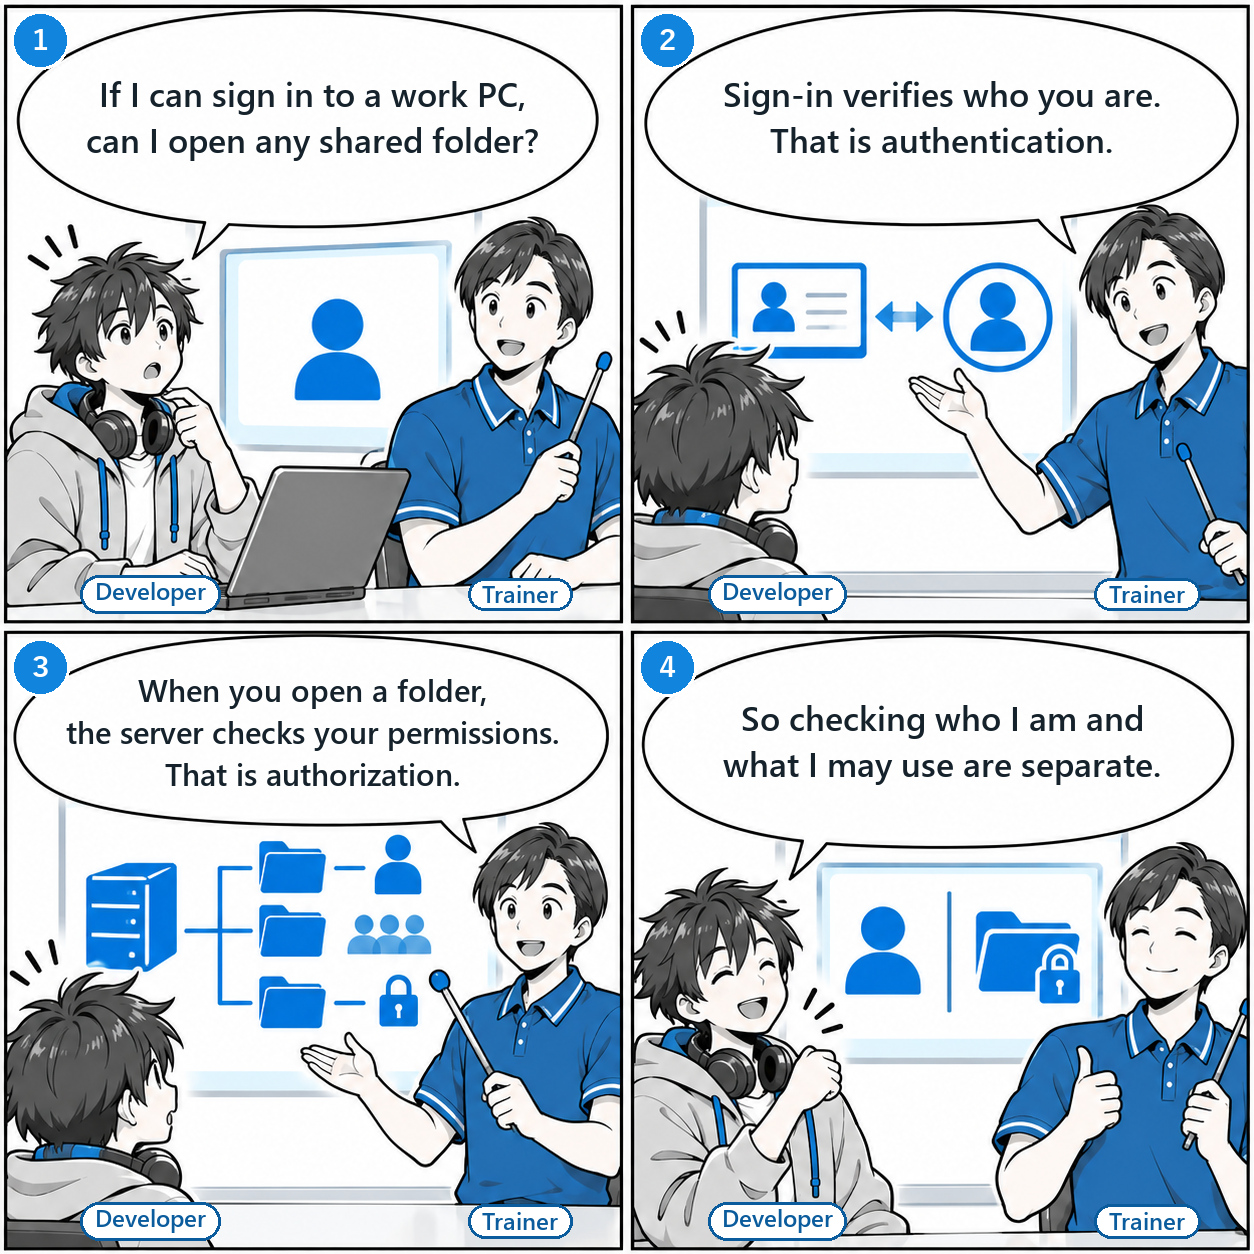
- Developer“If I can sign in to a work PC, can I open any shared folder?”
- Trainer“Sign-in verifies who you are. That is authentication.”
- Trainer“When you open a folder, the server checks your permissions. That is authorization.”
- Developer“So checking who I am and what I may use are separate.”
AD is infrastructure for managing account information shared across an organization.
This series covers Active Directory Domain Services (AD DS) in Windows Server. It stores information about users, computers, groups, and other objects in a directory and makes it available within the organization.
Shared account information lets integrated systems work with the same users. However, having an account and being allowed to use a particular file are different things.
Separate identity verification from access permissions
Authentication verifies identity; authorization decides whether an operation is allowed.
For a shared folder, the file server checks access rights using the authenticated user and group memberships. Merely setting a department attribute to “Accounting” does not grant access to an accounting folder.
| Role | What it checks in shared-folder access |
|---|---|
| Authentication | Who the user is. Verify identity using a domain account. |
| Authorization | Whether that user may perform an operation. Decide whether reading or writing is allowed by permissions assigned to users or groups. |
Supporting SSO and centralized settings
Single sign-on (SSO) reduces repeated credential entry across integrated services.
With Windows Kerberos authentication, a client can obtain the tickets needed for services after logon and use them to demonstrate the user’s identity to supported services. Each service’s permission settings determine what the user may do.
Administrators can apply settings collected in Group Policy Objects (GPOs) to users and computers. GPO links and applicability conditions determine the targets, with processing at times such as startup, logon, and background refresh.
It is easier to understand AD when you distinguish account information, identity verification, access rights, and the application of settings.
1.1.2 Managing users, computers, and groups
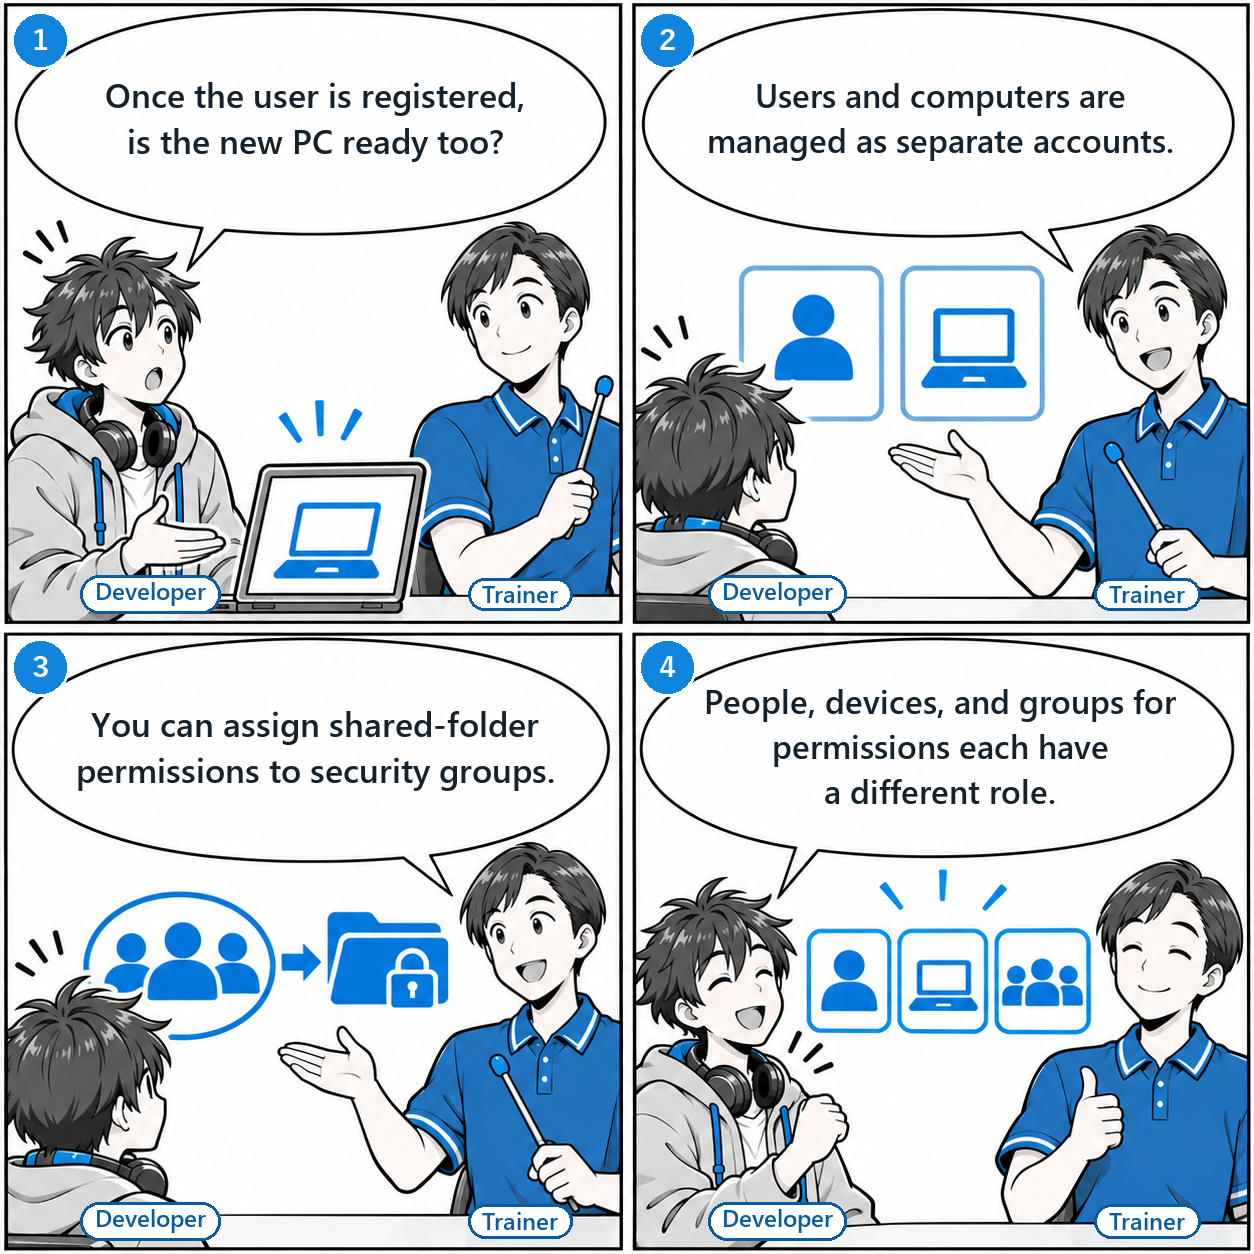
- Developer“Once the user is registered, is the new PC ready too?”
- Trainer“Users and computers are managed as separate accounts.”
- Trainer“You can assign shared-folder permissions to security groups.”
- Developer“People, devices, and groups for permissions each have a different role.”
Users, devices, and groups used to assign permissions are managed as distinct objects.
A user account identifies a user, while a computer account identifies a computer that joins the domain. Registering a user does not, by itself, join a device to the domain or complete its configuration.
| Object | Main role |
|---|---|
| User | Manage an identity and its account information |
| Computer | Manage the identity of a domain-joined computer |
| Security group | Collect accounts and other members for assigning permissions and user rights |
| Organizational unit (OU) | Organize objects, delegate administration, and design Group Policy scope |
Groups and OUs serve different purposes.
A security group can be used when assigning access to a shared folder. Moving an object into an OU or changing its department attribute does not automatically grant that folder’s permissions.
An OU structure need not copy the organization chart. Design it around who will administer the objects and which users or computers should receive particular settings.
1.1.3 The role of domain controllers
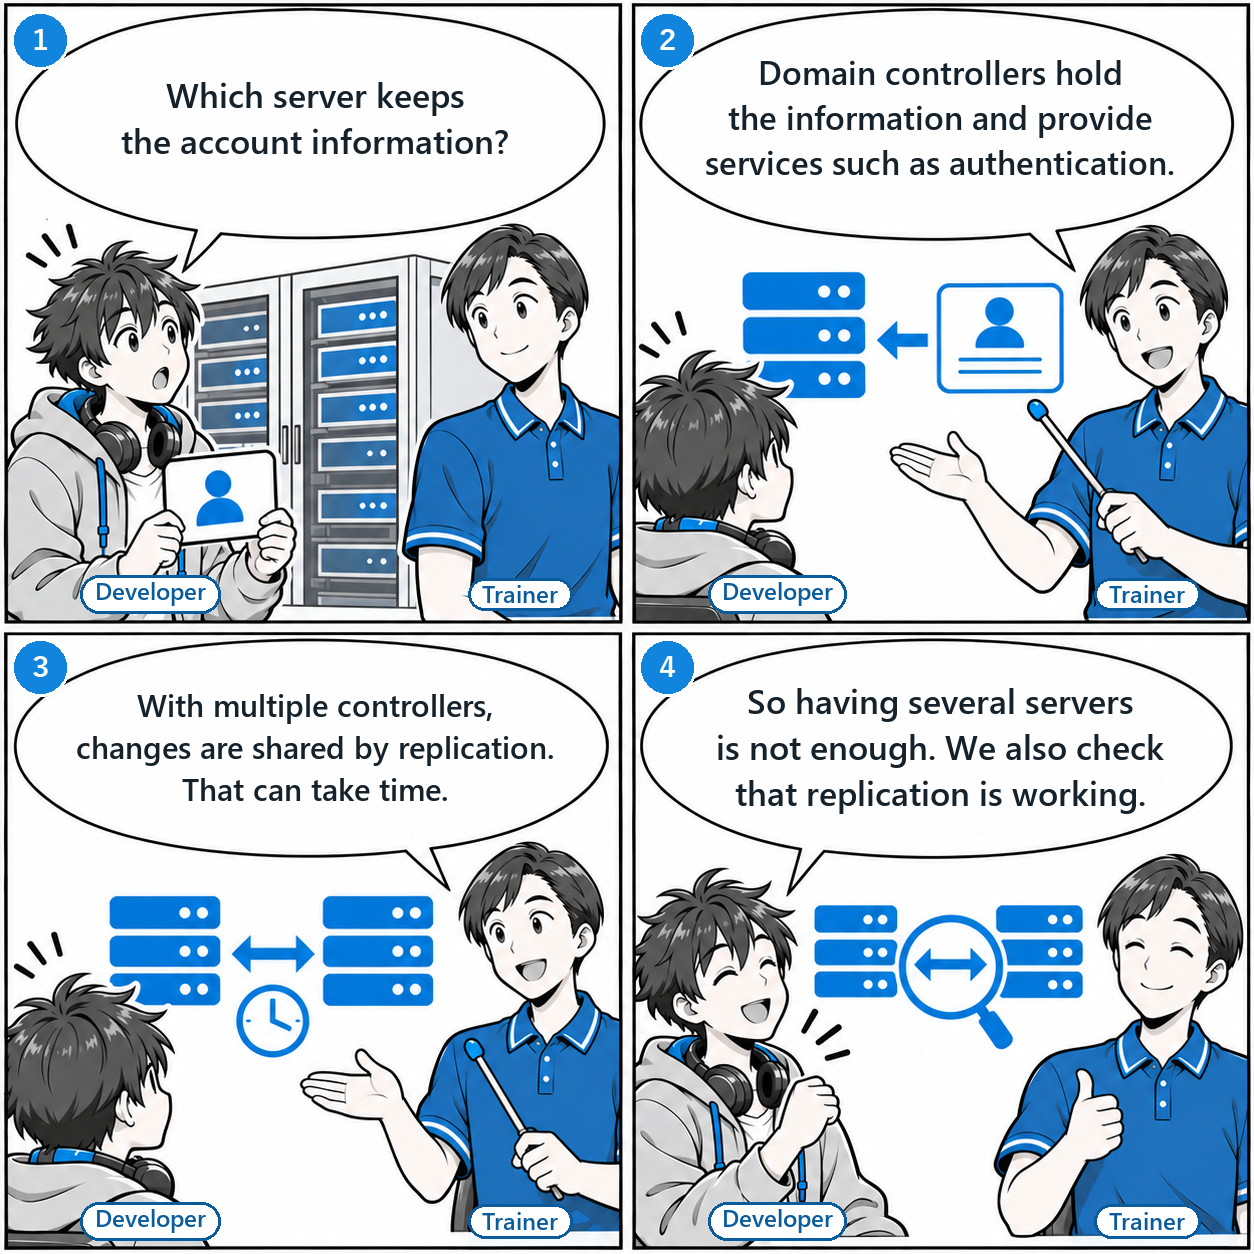
- Developer“Which server keeps the account information?”
- Trainer“Domain controllers hold the information and provide services such as authentication.”
- Trainer“With multiple controllers, changes are shared by replication. That can take time.”
- Developer“So having several servers is not enough. We also check that replication is working.”
A domain controller (DC) stores directory information and provides services such as authentication.
AD DS replicates the relevant directory information between DCs. Changes take time to reach other DCs, so the information returned can differ depending on the DC while replication is in progress.
Deploying multiple DCs is part of preparing for a server outage. Availability also depends on functioning replication, name resolution, and network paths, not simply the number of servers.
Do not assume that every DC always holds all data for the entire organization. Check which information is replicated where, and continue monitoring replication after adding a DC.
1.2 Active Directory and DNS
1.2.1 Why AD needs DNS
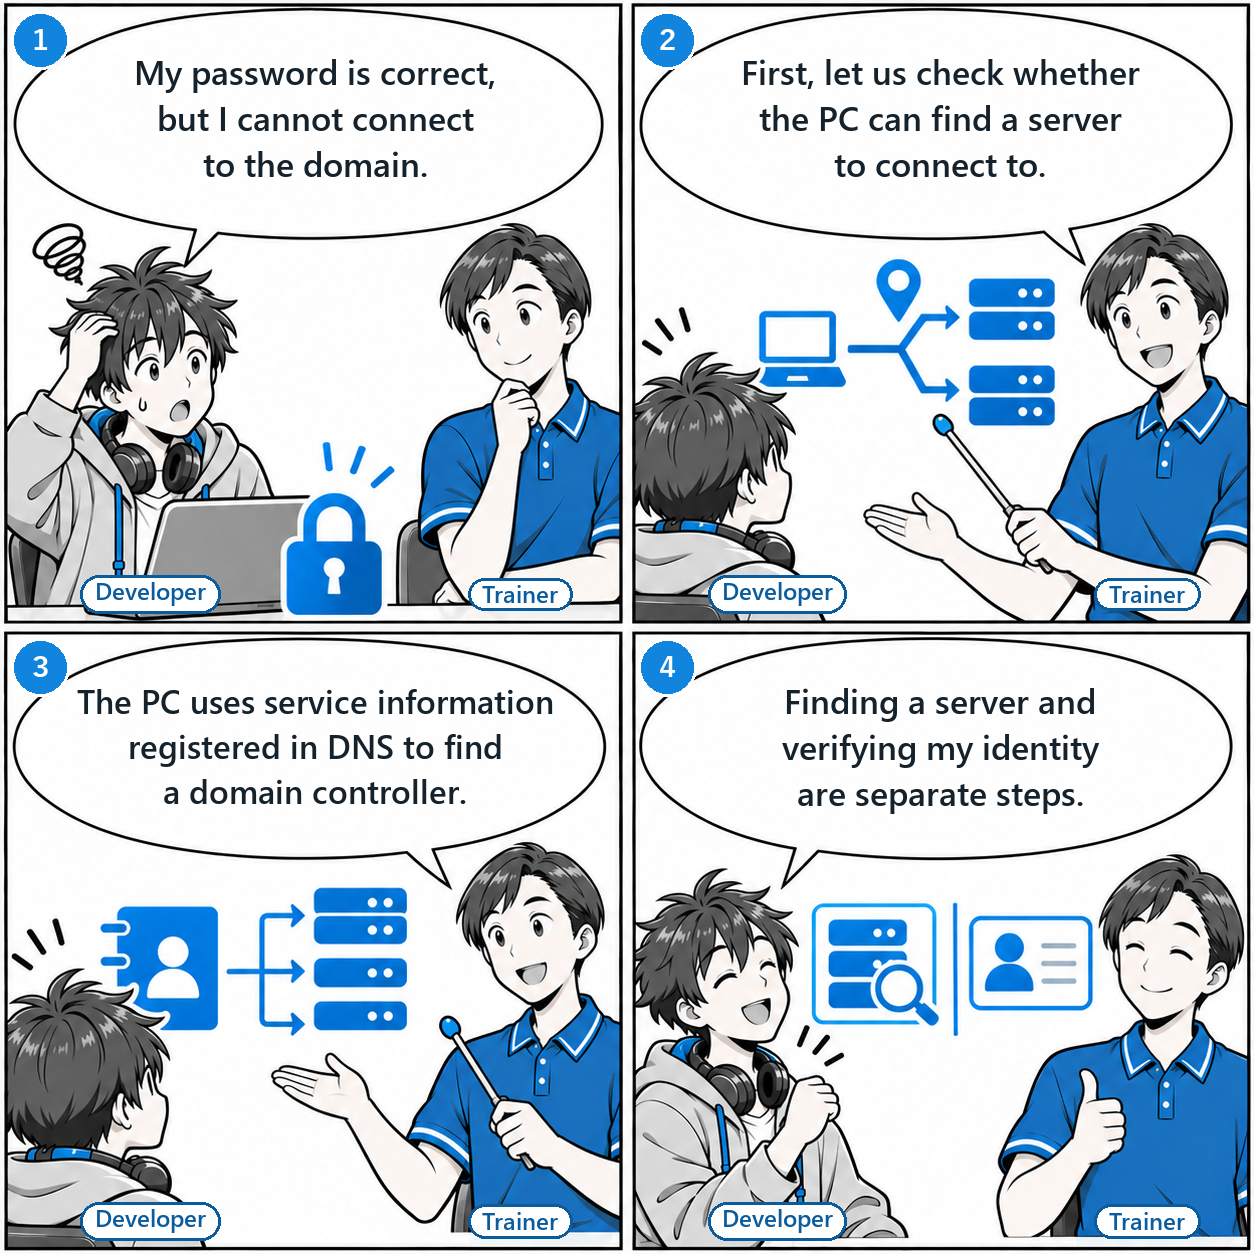
- Developer“My password is correct, but I cannot connect to the domain.”
- Trainer“First, let us check whether the PC can find a server to connect to.”
- Trainer“The PC uses service information registered in DNS to find a domain controller.”
- Developer“Finding a server and verifying my identity are separate steps.”
Before authentication can begin, the client needs to find a server to contact.
DNS (Domain Name System) provides information about hosts and services by name. Windows DC Locator uses records such as SRV records registered in DNS to find candidate DCs.
After finding candidates, it contacts DCs to check their responses and capabilities. DNS does not verify a user’s password; server discovery and identity verification are separate stages.
- 1The PC queries DNS for information about the DC it needs.
- 2It contacts candidates found through DNS to locate an available DC.
- 3It performs the required operations, such as logon, with the selected DC.
Site-specific records also help locate an appropriate DC. Understand AD site configuration together with DC Locator, rather than assuming that DNS automatically identifies the nearest office from an IP address alone.
1.2.2 How AD-integrated DNS works
AD-integrated DNS stores DNS zone data in AD DS and replicates it through AD.
A DNS zone is a unit for managing a portion of the DNS namespace. An AD-integrated zone shares its data using the AD replication mechanism.
DNS servers on writable DCs holding the AD-integrated zone can accept updates to it. Configuration determines the replication scope; a zone is not unconditionally copied to every DC in the forest.
| Mechanism | What it does |
|---|---|
| AD-integrated zone | Determines where DNS data is stored and how it is replicated |
| Dynamic update | Allows clients or DHCP servers to request record additions and changes |
| Secure dynamic update | Controls updates using the identity and permissions of the updating principal |
AD integration and dynamic update do not mean the same thing. Creating a user account also does not automatically create a DNS record for that user.
1.2.3 The role of SRV records
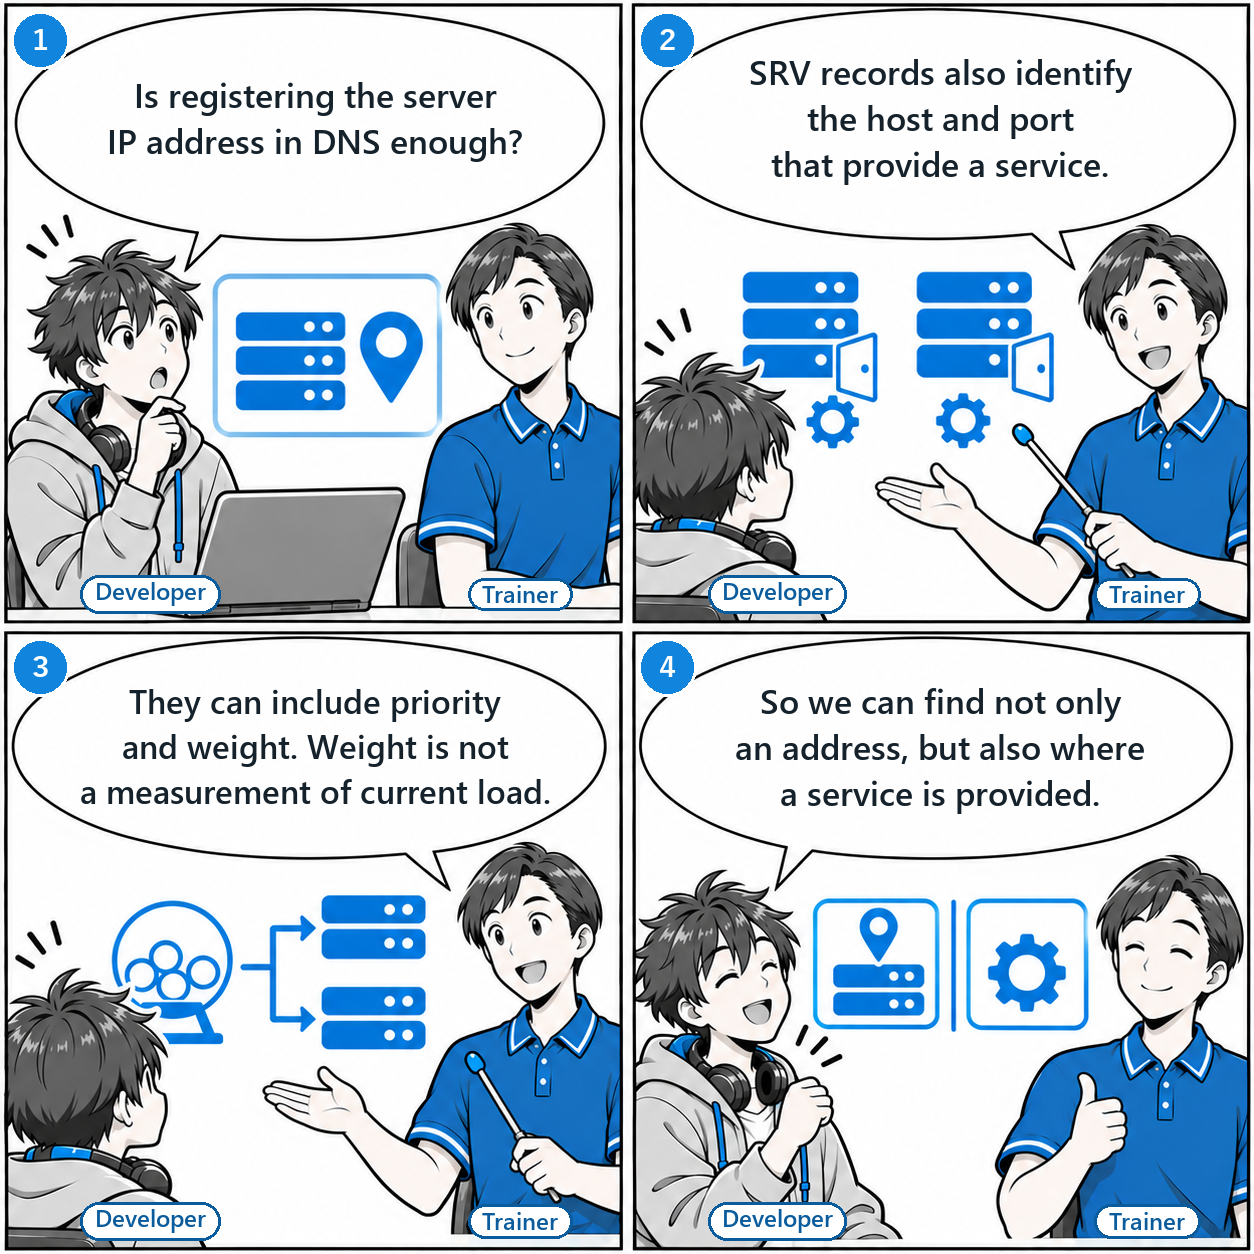
- Developer“Is registering the server IP address in DNS enough?”
- Trainer“SRV records also identify the host and port that provide a service.”
- Trainer“They can include priority and weight. Weight is not a measurement of current load.”
- Developer“So we can find not only an address, but also where a service is provided.”
An SRV record identifies the host and port providing a service.
A and AAAA records resolve host addresses, whereas SRV records locate services. DC Locator uses SRV records for services such as LDAP.
LDAP is a protocol for accessing a directory. In this context, LDAP is one of the services involved in DC discovery, rather than simply an “authentication service.”
The following illustrative DNS zone-file entry uses the reserved example domain example.com. These are not the configuration values of an actual organization.
_ldap._tcp.example.com. 600 IN SRV 0 100 389 dc01.example.com.| Field | Value and meaning in this example |
|---|---|
| Name | _ldap._tcp.example.com. identifies the LDAP service over TCP for the domain |
| TTL and class | 600 is the cache lifetime in seconds; IN denotes the Internet class |
| Priority | 0. Lower numbers are preferred |
| Weight | 100. A relative weight for selecting among records with the same priority |
| Port and target | 389 and dc01.example.com. identify the service port and hostname |
Weight is not a measurement of current CPU utilization or connection count. Distinguish SRV selection rules from the application’s discovery and connection behavior.
1.2.4 Dynamic DNS updates
Dynamic updates allow changes such as new addresses to be reflected in DNS.
Windows DNS clients attempt record updates at events such as startup or address changes. In a DHCP environment, client and DHCP server settings determine which party updates A and PTR records.
- 1Relevant information changes, such as the device name or address.
- 2The DNS client or DHCP server requests an update according to its configuration.
- 3The DNS server checks the update conditions and permissions, then updates authorized records.
An authenticated device is not allowed to overwrite any name it chooses.
Secure dynamic updates involve access control on records and other relevant objects as well as authentication. Connecting to a VPN does not guarantee automatic registration; check adapter and name-registration settings.
When investigating name-resolution problems, compare the current address, DNS records, and the principal making updates. Check the actual update configuration, including how stale records are handled.
1.3 Authentication protocols
1.3.1 Kerberos authentication
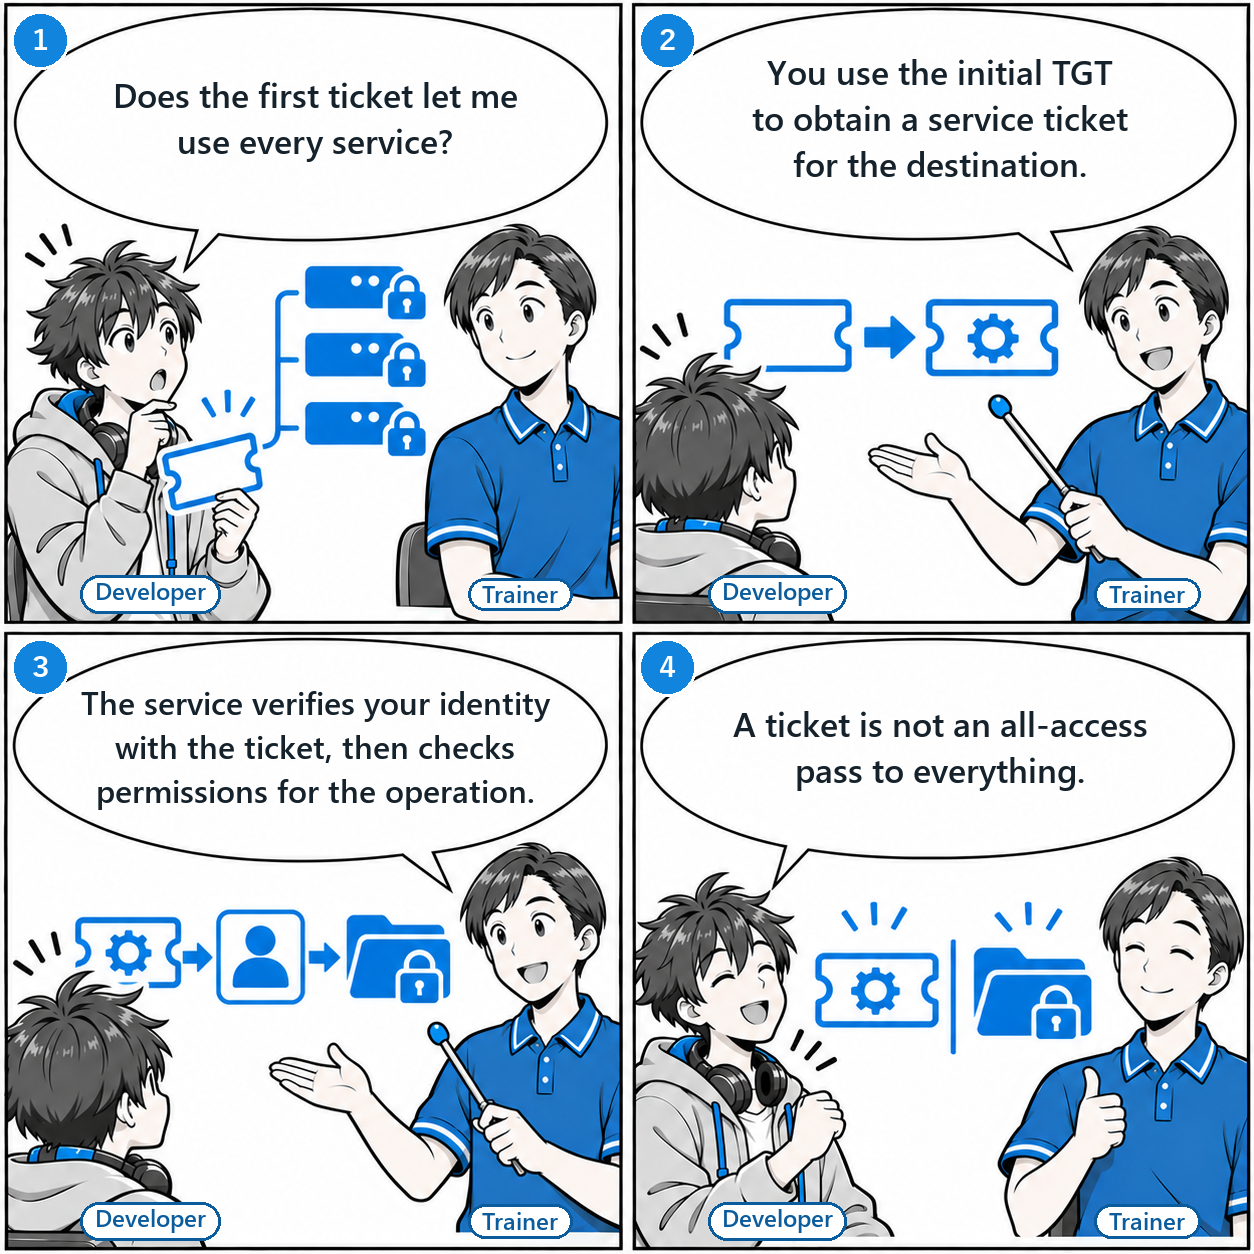
- Developer“Does the first ticket let me use every service?”
- Trainer“You use the initial TGT to obtain a service ticket for the destination.”
- Trainer“The service verifies your identity with the ticket, then checks permissions for the operation.”
- Developer“A ticket is not an all-access pass to everything.”
Kerberos uses tickets to demonstrate a client’s identity to a service.
In a Windows domain, the Key Distribution Center (KDC) on a DC issues tickets. A client obtains a Ticket Granting Ticket (TGT) and can use it to request a ticket for the destination service.
Tickets reduce the need for users to enter a password each time they connect to a supported service. A service can verify the ticket; it does not necessarily ask a DC to verify identity for every connection.
Having a ticket does not grant access to every function of the service. The file server or application decides which operations the user or their groups are permitted to perform.
1.3.2 NTLM authentication
NTLM is an authentication protocol based on challenge and response.
The client responds to the server’s challenge using information derived from the password. The NTLM authentication exchange does not send the password itself in plain form.
For a domain account, the server can pass validation to a DC. Local accounts are validated against local information, so it is inaccurate to say NTLM always contacts a DC for every access.
| Question | What to examine |
|---|---|
| Why NTLM is being used | Application support, the way the destination is specified, and authentication settings |
| Migrating to Kerberos | NTLM dependencies and support in each application |
| Restricting NTLM | Audit existing usage, then test the impact of restrictions |
When you find NTLM in use, investigate why it was selected for that connection. Do not disable it across the board without checking the effects on existing services.
1.3.3 Basic authentication
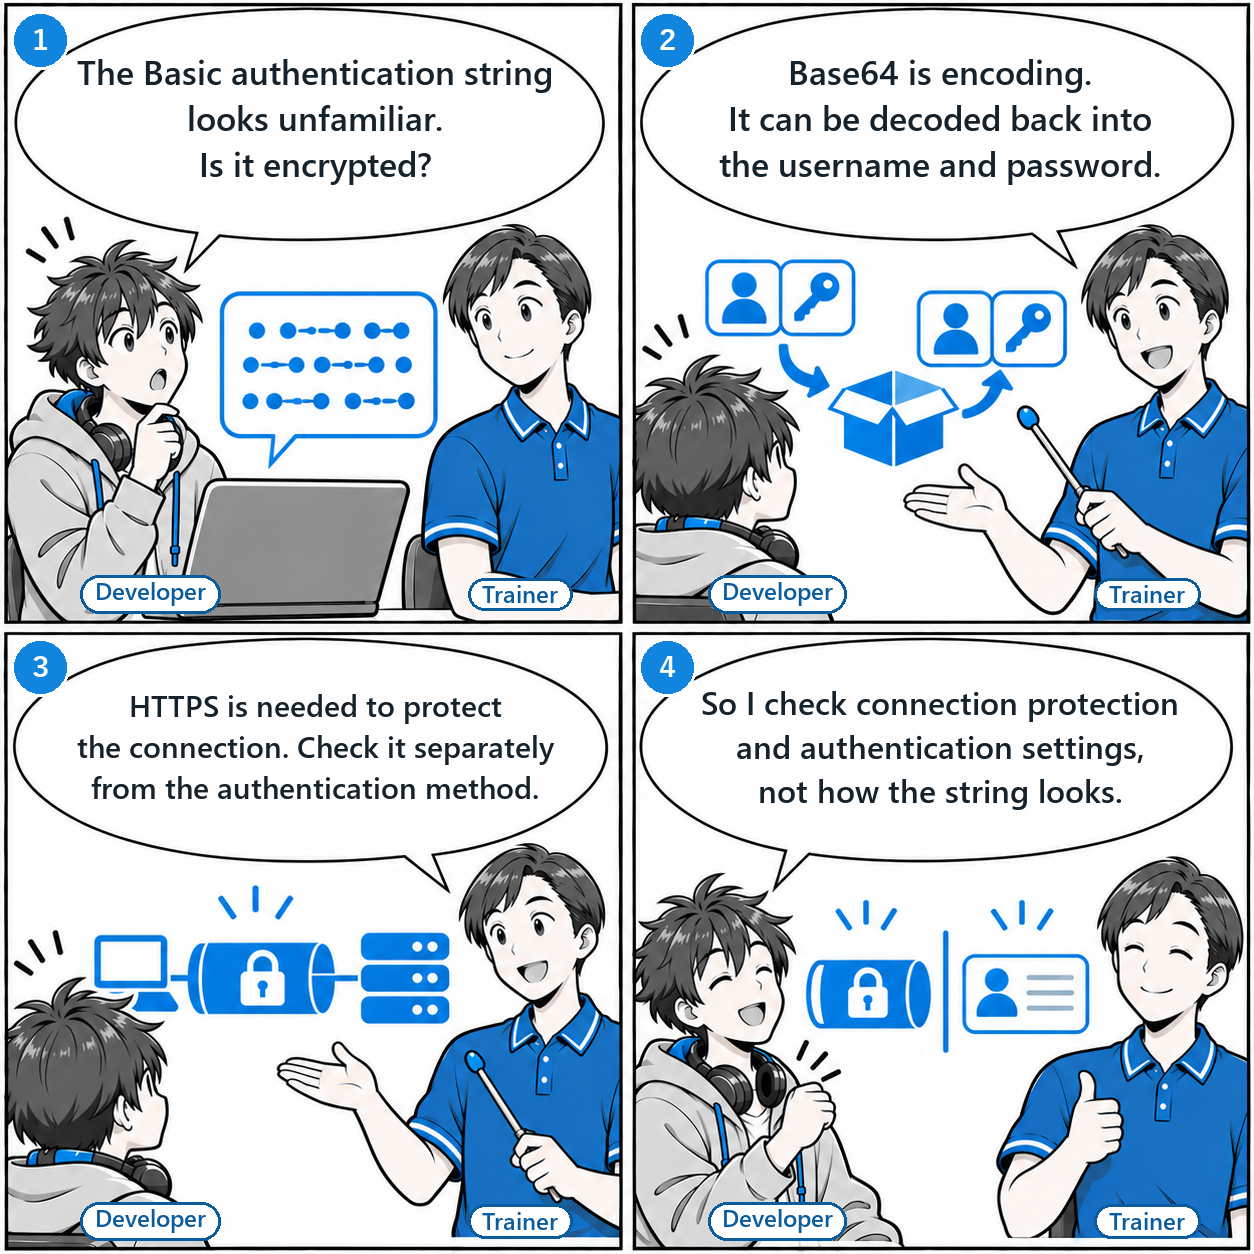
- Developer“The Basic authentication string looks unfamiliar. Is it encrypted?”
- Trainer“Base64 is encoding. It can be decoded back into the username and password.”
- Trainer“HTTPS is needed to protect the connection. Check it separately from the authentication method.”
- Developer“So I check connection protection and authentication settings, not how the string looks.”
Basic is an HTTP authentication scheme, and its Base64 encoding is not encryption.
The client combines a username and password, Base64-encodes them, and sends the result as credentials. Anyone who obtains the encoded value can reverse the encoding, so Basic itself does not conceal the communication.
| Mechanism | Role |
|---|---|
| Basic authentication | Carries credentials in an HTTP request |
| Base64 | A reversible encoding that represents data as another string |
| HTTPS | Protects the communication channel using TLS |
If Basic authentication is used for sensitive information, protection such as HTTPS is necessary. HTTPS protects the channel; it does not replace proper credential handling at the receiving system or access-control design.
Basic is not a final fallback that AD automatically selects for external connections. Check the client and server settings for the authentication schemes that the HTTP service provides.
1.3.4 Choosing authentication methods
Assess authentication methods together with application support and connection conditions.
Windows Negotiate selects Kerberos or NTLM. There is no universal automatic sequence that falls back from Kerberos to NTLM and then to Basic for every connection.
| Scenario | How to assess it |
|---|---|
| A connection supporting Windows integrated authentication | Check whether Kerberos can be used and determine which method was actually selected |
| A host specified by IP address | Windows does not attempt Kerberos by default. Special configuration can provide exceptions; normally, configure DNS names and service identity information appropriately |
| A connection through a VPN | Check DNS, reachability, and authentication settings after connecting. The VPN alone does not guarantee a particular method |
| A connection to an HTTP service | Check the schemes offered by the service and channel protection. Being internal or external alone does not determine the method |
An order for investigating authentication problems
When a connection fails, separate discovery, communication, authentication, and permissions instead of assuming the password is wrong. The following sequence organizes the roles covered in this chapter.
- 1Identify the service and the name used to connect to it.
- 2Check DNS discovery and connectivity to the required endpoints.
- 3Check the methods offered by the application and the method recorded in logs.
- 4If Kerberos is expected, check connection conditions and settings such as the service principal name (SPN).
- 5If identity verification succeeds but access is denied, inspect permissions.
Distinguishing “the destination cannot be found,” “identity verification failed,” and “the operation is not permitted” is a starting point for understanding systems that use AD. The next installment explores structures such as domains and forests.
Company-wide AI security—we can help, from the foundations to day-to-day operations.
From foundations such as identity and access management to LLM-specific risks (prompt injection, data leaks, harmful output)—using AI safely across an organization involves a wide range of issues.
We develop and provide our own LLM auditing product, "LLM-Audit". Drawing on that expertise, we provide practical support from audits and assessments through defenses and safe operational design.
Explore our LLM security services →