Understanding Active Directory: The Technology Behind Enterprise AI Security - Part 2: Building the Domain Environment
Hello! In Part 1, we explored how Active Directory, DNS, and authentication work together. This time, we look at building the domain environment that supports them.
We will work through the key decisions in order. Choose names, promote a Windows Server to a domain controller, and make sure clients use DNS resolvers that can find AD services.
The focus is Active Directory Domain Services (AD DS) on Windows Server. The comics are fictional teaching conversations, not accounts of actual deployments.
Series Overview
- Chapter 1: Understanding the basics - Fundamentals of Active Directory and Kerberos/NTLM authentication
- [★This installment★] Chapter 2: Building a domain environment - Setting up a lab environment
- Chapter 3: Joining clients and servers to the domain - Domain join in detail
- Chapter 4: Proxy servers and Integrated Windows Authentication
- Chapter 5: Browser configuration and authentication - Settings for each browser
- Chapter 6: Troubleshooting - Common problems and solutions
- Chapter 7: Security and best practices - Considerations for production environments
- Chapter 8: Practical configuration examples - Integration with AI security tools
2.1 Designing domain names
2.1.1 Distinguish DNS names from NetBIOS names
- Developer“Can I use just the company name for the domain?”
- Trainer“Choose a DNS name and a short NetBIOS name.”
- Trainer“The two names have different length limits.”
- Developer“I will check each name and its limits separately.”
An AD domain has both a DNS name and a short NetBIOS name.
For example, the DNS name might be corp.example.com and the NetBIOS name CORP. The former is used for DNS-based name resolution, while the latter appears in traditional forms such as CORP\user.
| Name | Limit to check |
|---|---|
| AD domain DNS name | Up to 64 characters for the full AD domain name. Do not confuse this with the general DNS limit. |
| Each DNS label | Up to 63 bytes for each part separated by a dot. |
| NetBIOS domain name | 1 to 15 characters. Check it separately from the DNS name. |
For interoperability, use letters, digits, and hyphens as your basic naming choices. Avoid names tied to departments or locations that may change. A name being technically accepted does not make it a good long-term choice.
2.1.2 Why avoid .local for a new domain?
- Developer“Should I use .local for internal names?”
- Trainer“.local is a special name used by mDNS.”
- Trainer“For new AD domains, use a name under a domain you own.”
- Developer“Internal names need to avoid conflicts too.”
.local does not simply mean “internal use.”
Names ending in .local have special treatment in Multicast DNS (mDNS), which resolves names on the local link. Using the same suffix in conventional DNS can introduce differences in how devices and applications resolve names.
This does not mean every existing .local environment will stop working. Choose names that avoid conflicts for new deployments, and assess the effects of renaming and the available alternatives before changing an existing environment.
2.1.3 Use a namespace under a domain you own
A common starting point is a subdomain of a registered domain that your organization controls.
For illustration, suppose example.com represents that registered domain. You could use corp.example.com for AD. In a real design, substitute a domain your organization owns and manages.
If the public website and AD use the same namespace, plan how internal and external records will be maintained. Returning different internal and external answers for the same name is known as split DNS.
| Choice | What to plan |
|---|---|
| Subdomain of an owned domain | Separate its purpose from public names, and establish who manages it and how queries reach it. |
| Same internal and external namespace | Ensure internal DNS can also resolve public service names through appropriate records or query paths. |
| An internal-use name such as .internal | Evaluate it for the intended use. Reservation alone does not settle AD naming or cloud integration. |
In 2024, ICANN reserved .internal for private-use applications by deciding it would never be delegated in the DNS root. You still need to plan AD names, user sign-in names, and public service names separately.
Using internal names does not, by itself, prevent access. Network access and exposure must be controlled separately from DNS.
2.1.4 Plan for organizational changes and cloud integration
- Developer“Must I rename AD to connect it to the cloud?”
- Trainer“Users can have a different sign-in suffix.”
- Trainer“Verify that suffix domain in the cloud directory.”
- Developer“I will plan AD names and sign-in names separately.”
Separate the AD domain name from the sign-in name a person enters.
A User Principal Name (UPN) is a sign-in name such as user@example.com. You can add a UPN suffix, the part after @, that differs from the AD DNS domain name.
Adding a suffix and changing individual users’ UPNs are separate operations. Check the effects on existing applications and sign-in before applying the change to users.
When synchronizing with Microsoft Entra ID, plan to verify that suffix domain in Entra as well. An existing .local AD name does not, on its own, make renaming the entire AD domain mandatory.
A new department or office does not automatically require another AD domain.
Consider organizational units (OUs) for delegated administration and policy scope, and sites for network locations and replication. OUs organize directory objects; sites describe network divisions based on subnets and related configuration.
| Design information to retain | Questions to answer |
|---|---|
| Name ownership | Who manages registered domains, DNS zones, and UPN suffixes? |
| Organizational changes | Can an OU or delegated permissions accommodate a department change? |
| Additional offices | How will subnets, sites, and connectivity to DCs be configured? |
| Cloud integration | What sign-in names, domain verification, and application changes are needed? |
2.2 The AD DS role and DC promotion
2.2.1 What installing the role provides
A Windows Server role is a function the server provides.
Adding the AD DS role installs the components needed to configure a domain controller. Include the appropriate management tools, but remember that installing the role does not complete DC configuration.
- 1Open Add Roles and Features in Server Manager.
- 2Check the target server and add Active Directory Domain Services and the required management tools.
- 3Check the installation result, then proceed to domain controller promotion.
Before installation, check whether the server is in a workgroup or already joined to a domain. A server that is not domain-joined is not a member server.
2.2.2 Choose a new environment or an existing one
- Developer“Does installing AD DS make this server a DC?”
- Trainer“After installing the role, promote the server to a DC.”
- Trainer“Choose a new forest or the appropriate existing setup.”
- Developer“After promotion and restart, I will check the setup.”
Promotion determines which AD environment the server will join or create.
A forest contains one or more domains that share information such as the schema. Creating the first environment and adding a DC to an existing domain require different choices and prerequisites.
For a new forest, specify the root domain name. Review settings such as DNS, and configure a password for Directory Services Restore Mode (DSRM) that can be managed securely.
After promotion and restart, check domain information, DNS registration, and shares such as SYSVOL and NETLOGON. If you added a DC to an existing domain, also check replication with the other DCs.
Finishing the wizard does not prove that clients can use the environment. Verify the paths clients actually need, including name resolution, DC connectivity, domain join, and sign-in.
2.2.3 Place roles according to their failure impact
DCs, DNS, and DHCP have different responsibilities.
| Role | Placement considerations |
|---|---|
| Domain controller | Provides authentication and directory services. With multiple DCs, avoid a layout that lets one failure stop all of them. |
| DNS | Resolves the names AD requires. DNS can run on a DC, but every DC does not have to host the DNS server role. |
| DHCP | Distributes client IP settings. Consider whether maintenance or a failure would interrupt it alongside authentication. |
Staff count alone cannot decide whether one server is enough or whether roles must be separated. Compare downtime tolerance, operational capacity, maintenance procedures, and recovery requirements against the advantages of combining roles.
Writable DCs are normally peers that accept directory updates and replicate changes. They are not simply a primary that accepts all writes and a backup that waits idle.
Virtualization still requires a recovery plan.
Placing several DCs on the same virtualization host can make them unavailable together if that host fails. Consider host and storage failure boundaries when deciding placement.
Supported virtualization platforms provide DC restore safeguards through VM-Generation ID. Those safeguards do not make snapshots a substitute for AD backup and recovery procedures.
2.3 Connecting DHCP and DNS configuration
2.3.1 DHCP distributes more than an IP address
DHCP leases IP configuration to clients for a limited period.
Define the address pool as a scope, and keep it separate from addresses assigned statically to servers and other devices.
| Information supplied | Purpose |
|---|---|
| IP address and subnet mask | The client address and its network boundary. |
| Router (option 3) | The default path to other networks. |
| DNS servers (option 6) | Resolvers to query for names. |
| Domain name (option 15) | A DNS domain name supplied to the client. It does not join the computer to AD. |
Receiving a domain name through DHCP does not create a computer account or perform an AD domain join. Network configuration and domain membership are separate operations.
Consider a DHCP relay when requests must reach a server on another subnet. A client broadcast does not simply pass through a router to that remote server.
2.3.2 Distribute resolvers that can resolve AD names
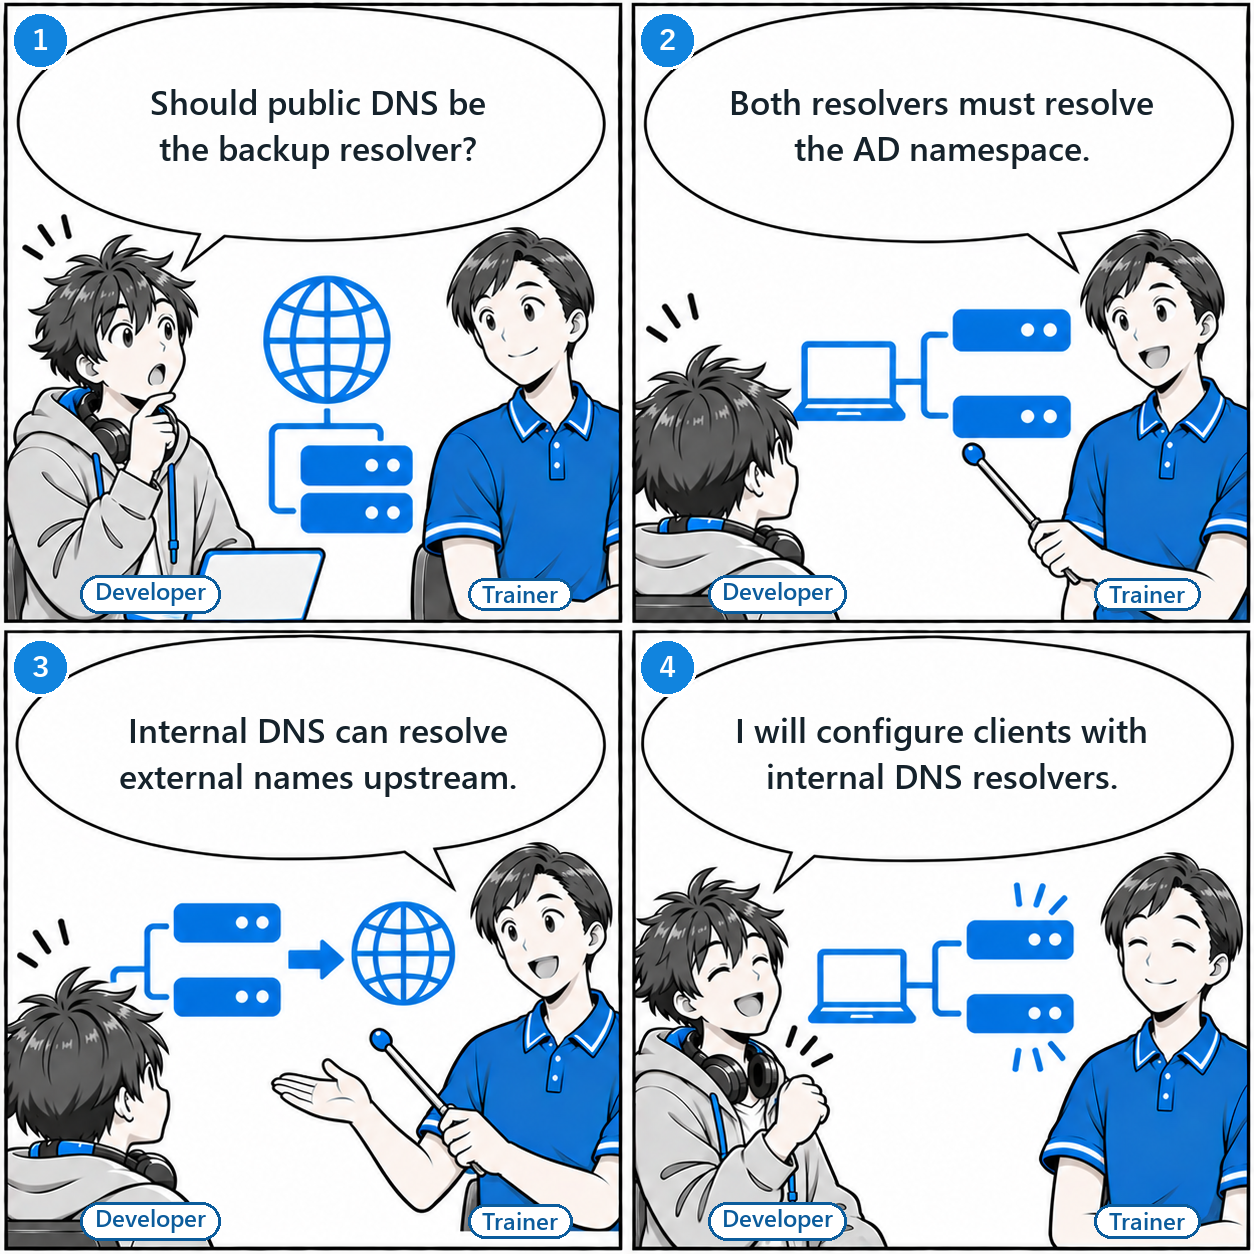
- Developer“Should public DNS be the backup resolver?”
- Trainer“Both resolvers must resolve the AD namespace.”
- Trainer“Internal DNS can resolve external names upstream.”
- Developer“I will configure clients with internal DNS resolvers.”
All DNS resolvers supplied to a client must be able to resolve the AD namespace.
Mixing in public DNS as a backup does not make it a replacement for resolving internal AD names. When a Windows DNS client receives a name-does-not-exist response, it does not simply continue through the list of resolvers.
Internal DNS can use forwarders or other configured resolution paths for external names. After distributing the settings, verify resolution of both internal and external names.
In Windows Server DHCP, define the scope and exclusions, then configure options such as routers and DNS servers. Also check AD authorization for a Windows DHCP server used in an AD domain.
A router distributing the settings must supply the same required information.
The following explanatory fragment follows Yamaha’s command syntax. It uses .10 and .11 for DNS and .100 through .199 as the pool, keeping those fixed addresses outside the pool.
dhcp scope 1 192.168.1.100-192.168.1.199/24
dhcp scope option 1 router=192.168.1.1
dhcp scope option 1 dns=192.168.1.10,192.168.1.11
dhcp scope option 1 domain=corp.example.com
Separate multiple DNS addresses with commas. This is not a complete configuration to deploy unchanged. Check the model and firmware, DHCP enablement, and conflicts with existing scopes before configuring a device.
On some older firmware, redefining a scope removes associated options. Read back the configuration after a change, and check the values an actual client receives.
2.3.3 Plan DHCP placement and failover together
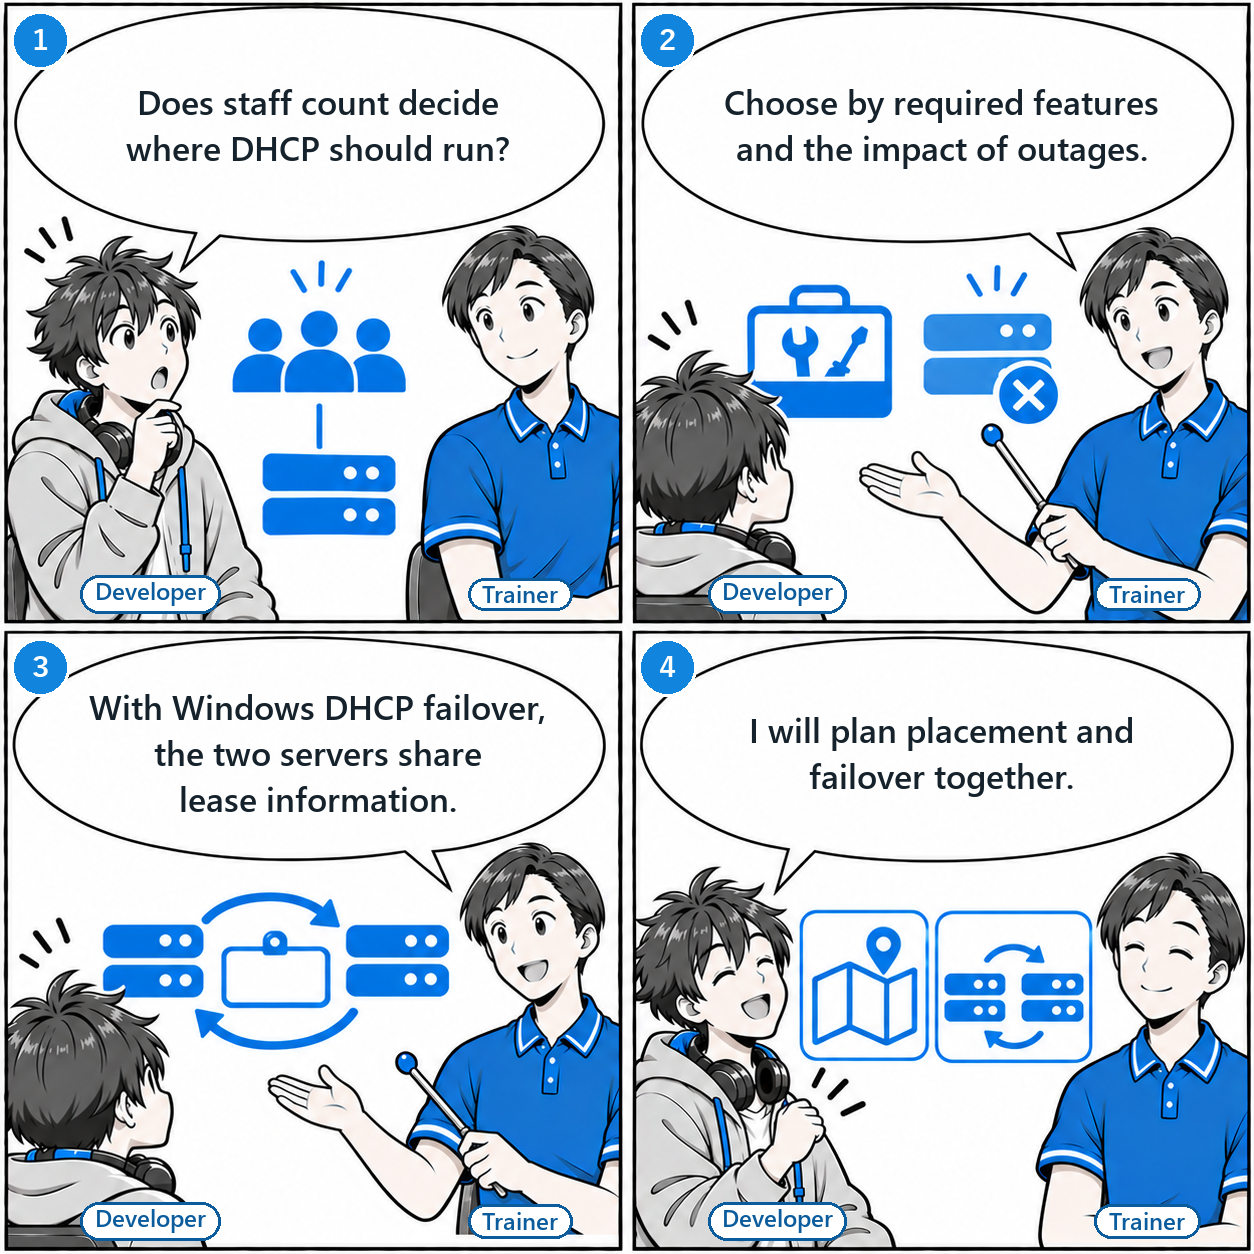
- Developer“Does staff count decide where DHCP should run?”
- Trainer“Choose by required features and the impact of outages.”
- Trainer“With Windows DHCP failover, the two servers share lease information.”
- Developer“I will plan placement and failover together.”
Decide both where DHCP runs and how service continues during an outage.
| Option | What to check |
|---|---|
| A router or other appliance | Confirm the specific model’s options, logging, reservations, and redundancy features. |
| A separate Windows DHCP server | Consider whether it separates maintenance and failure impact enough to justify the operational overhead. |
| DHCP on a DC | Check the combined outage impact and the credentials used for DNS updates. |
Windows Server DHCP failover lets two servers share lease information for IPv4 scopes. Choose load balancing or hot standby, and ensure relays can send requests to both servers when clients are on another subnet.
This differs from simply splitting an address pool between two servers. Lease sharing is also distinct from propagating scope configuration changes; perform the required configuration replication after making such changes.
If DHCP updates DNS on behalf of clients, plan its update credentials. When DHCP runs on a DC, review the use of a dedicated standard user account for DNS updates instead of letting those updates use the DC’s powerful credentials.
After setup, test new leases, lease renewal, behavior when one server is unavailable, and DNS registration. A running DHCP service alone does not demonstrate that clients receive the configuration they need.
Summary
Building a domain environment connects name design, DC promotion, and the DNS settings supplied to clients. Check the complete client path rather than judging success by an installed role or a running DHCP service.
Choose server placement according to outage impact and recovery requirements, not staff count alone. Retain the topology, configuration values, and verification procedures so they remain useful during expansion and troubleshooting.
Coming next
Part 3 covers joining client PCs and servers to the domain. We will explore how joining works, the steps involved, and what to check when it fails.
See you in the next installment!
Company-wide AI security — from foundations to operations, we can help.
From foundations such as identity and access management to LLM-specific risks (prompt injection, data leakage, harmful outputs) — using AI safely across an organization involves a wide range of considerations.
We develop and provide our own LLM auditing product, "LLM-Audit." Drawing on that expertise, we offer practical support spanning audits and assessments, defensive measures, and secure operational design.
Explore our LLM security services →