Understanding Active Directory: The Technology Behind Enterprise AI Security - Part 4: Proxy Servers and Integrated Windows Authentication
Hello! In Part 3, we covered domain membership and the checks that follow a join. This time, we connect AD identities to proxy authentication.
A proxy needs to distinguish the account that authenticated from the IP address that sent the traffic. The browser, authentication helper, AD and access rules each have a role in making that distinction.
This article covers an explicit forward proxy. The comics are fictional teaching conversations. Configuration snippets are examples, not evidence of a successful deployment or measured performance in our environment.
Series Outline
- Chapter 1: Understanding the basics - Fundamentals of Active Directory and Kerberos/NTLM authentication
- Chapter 2: Building a domain environment - Setting up a lab environment
- Chapter 3: Joining clients and servers to the domain - Domain join in detail
- [★This installment★] Chapter 4: Proxy servers and Integrated Windows Authentication
- Chapter 5: Browser configuration and authentication - Settings for each browser
- Chapter 6: Troubleshooting - Common problems and solutions
- Chapter 7: Security and best practices - Considerations for production environments
- Chapter 8: Practical configuration examples - Integration with AI security tools
4.1 Proxies and Windows Integrated Authentication
4.1.1 Separate domain membership from ticket validation
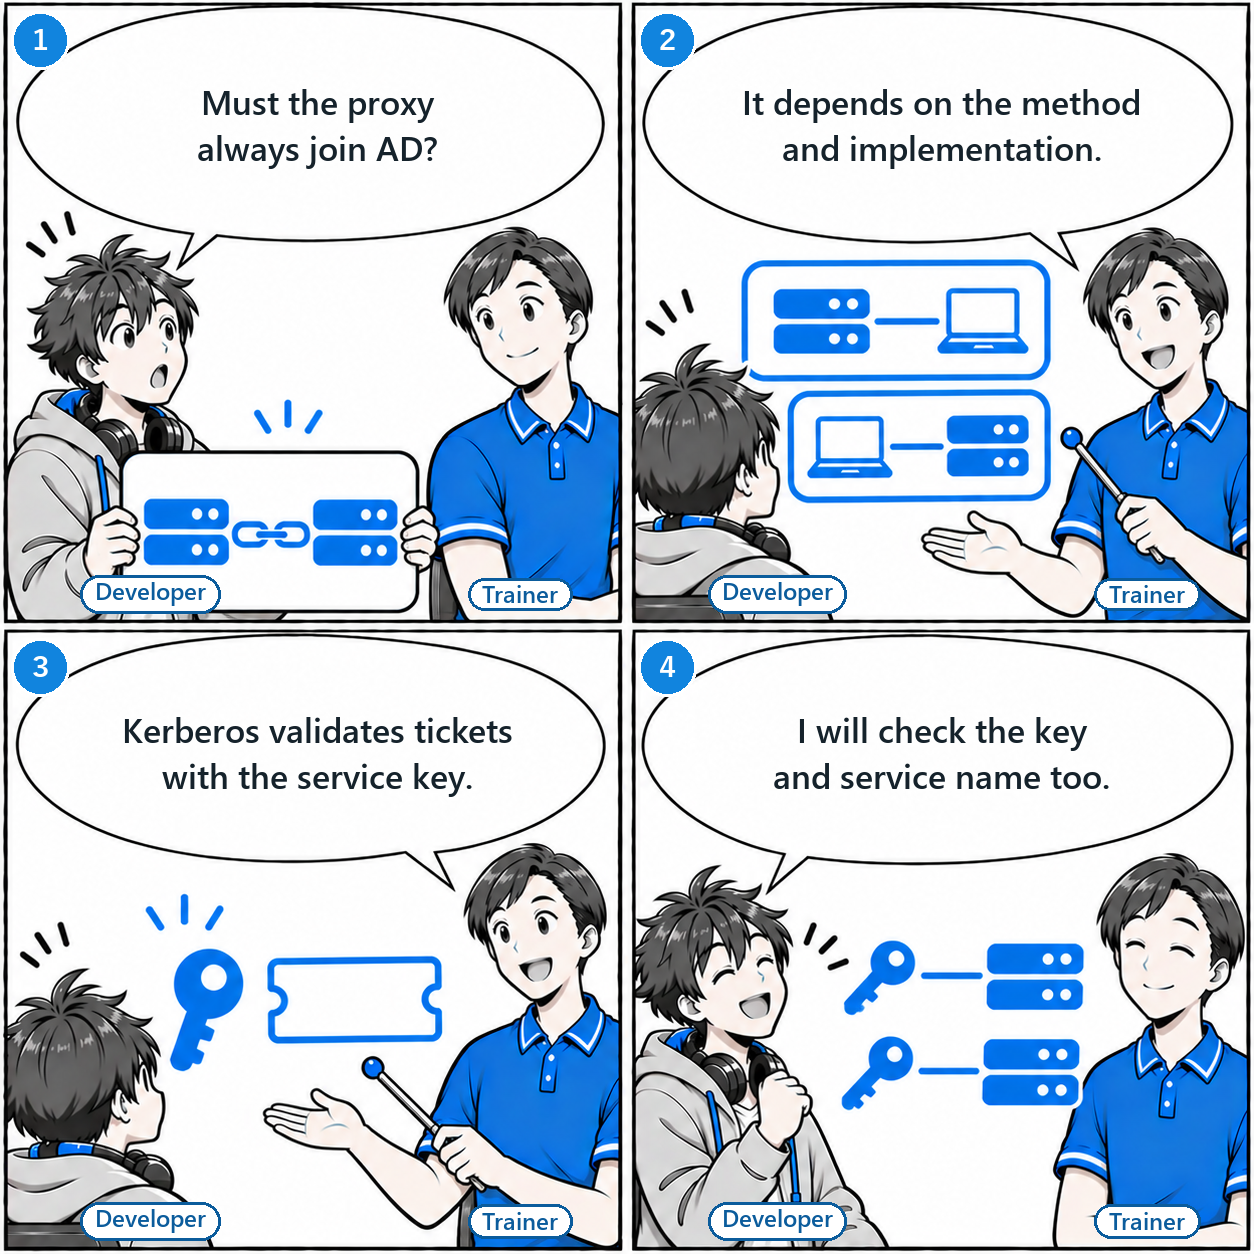
- Developer「Must the proxy always join AD?」
- Trainer「It depends on the method and implementation.」
- Trainer「Kerberos validates tickets with the service key.」
- Developer「I will check the key and service name too.」
The requirements for connecting a proxy to AD depend on the authentication method and its implementation.
In a Windows SSPI deployment, domain membership and the service account matter. A Kerberos acceptor can also obtain its service key from a keytab. Host domain membership itself is not the only possible basis for validating a service ticket.
| What to check | Why it matters |
|---|---|
| Proxy FQDN | The name used by clients must match the intended SPN |
| HTTP service SPN | The service name must map uniquely to the appropriate AD account |
| Keytab or service-account key | The acceptor needs the secret key, with protection and an update process |
| Domain membership | Check whether the chosen OS, helper and deployment procedure require it |
A Kerberos client obtains a service ticket from the KDC and presents it to the proxy. The service can validate it using its key. It does not necessarily send every ticket back to a DC for validation. PAC validation or group lookups can still require additional DC communication.
A keytab needs both protection against disclosure and a process that keeps it aligned with key changes in AD. The RHEL 9 example below follows that product’s documented deployment and assumes a domain-joined server.
4.1.2 The authentication exchange starts with a 407
- Developer「Does a VPN automatically mean NTLM?」
- Trainer「A VPN alone does not decide the method.」
- Trainer「Check names, connectivity, clients and policy.」
- Developer「I will check the cause before changing methods.」
The proxy advertises supported schemes, and the client responds using a supported method.
- 1For a request that needs authentication, the proxy returns
407 Proxy Authentication RequiredwithProxy-Authenticate. - 2The client proceeds according to the advertised schemes, its capabilities and its policy.
- 3The client sends authentication information in
Proxy-Authorization. Some methods need several exchanges. - 4The proxy evaluates authentication and access rules, then allows or denies the request.
| Method or term | How to interpret it |
|---|---|
| Negotiate | A negotiation framework. Windows SSPI can select Kerberos or NTLM. In Squid, also check the helper implementation |
| Kerberos | Needs the service name and key, usable tickets and the required connectivity |
| NTLM | Uses a challenge and response. Validating a domain account also requires a suitable server-side path to a DC |
| Basic | Sends a username and password. Do not enable it unconditionally when integrated authentication fails |
negotiate_kerberos_auth is a Kerberos helper. The word Negotiate does not mean that a particular helper also handles NTLM. An NTLM deployment needs a compatible helper or backend and policy that permits it.
Kerberos can work over a VPN when name resolution, the necessary connectivity and suitable tickets are available. It can also fail on an office LAN because of an SPN or policy issue. Network location alone does not determine the method.
Automatic credential submission also depends on browser support and management policy. If authentication prompts repeat, check the proxy route, advertised schemes, tickets and client configuration first.
4.1.3 Do not use an IP address as proof of identity
- Developer「Does the same IP mean the same user?」
- Trainer「Not on shared PCs or behind NAT.」
- Trainer「Record the authenticated name and source separately.」
- Developer「I will test what happens when users change.」
Traffic from the same IP is not necessarily traffic authenticated as the same account.
Several people can share a NAT address. A shared PC can keep its address while its user changes. There is no universal rule that binding an IP to a username for 30 minutes produces accurate attribution.
| Record or state | What to distinguish |
|---|---|
| Authenticated account name | Which request or connection the authentication result belongs to |
| Source IP and timestamp | Useful evidence about traffic, but not proof of a person by itself |
| Connection or authentication cache | Lifetime and reuse depend on the method, browser and proxy settings |
| Account in the AI service | It may differ from the account authenticated to the proxy |
Existing processes, connections or saved credentials can remain after a user change. Changing a browser’s displayed profile name does not guarantee that every request uses a different authentication identity.
- 1Use separate test users and correlate the authenticated name, timestamp and request.
- 2On a shared PC, sign out and sign in, then verify the identity on new browser traffic.
- 3Test several devices behind the same NAT and verify that the system does not identify them by IP alone.
- 4Check rejection behavior for unauthenticated requests, a disabled test account and a source outside the allowed network.
A CONNECT tunnel to an HTTPS destination does not, by itself, reveal encrypted AI prompts or responses. Traffic attribution, content inspection and AI-service audit logs are separate design concerns. This article does not configure TLS decryption.
4.2 Configure authentication in Squid
4.2.1 Verify the Windows build and its authentication support
- Developer「Does every Windows build use the same setup?」
- Trainer「Available helpers differ between builds.」
- Trainer「Check versions, authentication and maintenance.」
- Developer「I will verify old paths and instructions.」
Not every Windows Squid distribution supplies the same helpers or installation procedure.
Authentication features, bundled helpers, service registration and file locations differ by build and distribution. An old MSI filename or a fixed C:\Squid path is not a universal current installation recipe.
| Before installation | What to establish |
|---|---|
| Distributor and support scope | Whether the chosen Windows version is maintained |
| Squid version and build features | Whether the required authentication scheme is enabled |
| Bundled helpers | SSPI or Kerberos support, actual executable names and arguments |
| Service account | Access to keys and logs, and the AD service-name mapping |
| Configuration and log locations | Agreement between documentation and installed files |
Do not claim that Windows takes an hour and Linux takes a day without measuring a comparable deployment. Choose based on administration skills, the existing identity infrastructure, updates and monitoring.
The Linux configuration below cannot be copied directly to Windows. For Windows, confirm equivalent requirements in the current documentation for the selected distribution and in a test environment.
4.2.2 Align the Linux Kerberos prerequisites and ACLs
Configure the service name, key, helper and allowed traffic together.
This example follows the RHEL 9 documentation and assumes a server already joined to AD, with the Squid and Kerberos packages available. Package names and helper locations differ on Ubuntu and other distributions.
- 1Check DNS, time, the proxy FQDN and required network paths.
- 2Agree with the AD administrator on the HTTP service SPN, its account and key rotation. Use only the permissions needed for that work.
- 3Install the Squid keytab securely and verify that the service user can read it. Do not expose it to unrelated users.
- 4Configure the helper and access rules, then check the syntax.
- 5Test both successful authentication and rejection in an isolated environment before production rollout.
The following is an authentication-related excerpt. proxy.ad.example.com and AD.EXAMPLE.COM are example names, and 192.0.2.0/24 is a documentation network. Replace it with the actual authorized network. The helper path is the RHEL 9 example.
Do not replace the entire configuration with this excerpt and discard its existing protections. Keep restrictions for Safe_ports, SSL_ports, management functions, localhost and link-local destinations before the client access rules. An earlier unauthenticated allow localnet or allow all can bypass authentication, so review the complete rule order.
auth_param negotiate program /usr/lib64/squid/negotiate_kerberos_auth -k /etc/squid/HTTP.keytab -s HTTP/proxy.ad.example.com@AD.EXAMPLE.COM
auth_param negotiate children 10

acl corp_clients src 192.0.2.0/24
acl authenticated proxy_auth REQUIRED

http_access deny !corp_clients
http_access allow corp_clients authenticated
http_access deny all
An earlier http_access allow localhost also permits local requests before authentication. If local client traffic must authenticate too, review the allowed sources and rule order while distinguishing necessary management access from general proxy traffic.
children 10 is an example maximum helper count, not a performance recommendation. Tune it using observed load and helper behavior. The official configuration reference lists auth_param through Squid v7 and marks it unavailable in v8. Use the documentation for the version being deployed.
These commands inspect the version and configuration syntax. A successful parse does not prove AD authentication or traffic handling works.
squid -v
sudo squid -k parse4.2.3 Separate helper authentication from Squid authorization
- Developer「Does helper success allow every request?」
- Trainer「Authentication and authorization are separate.」
- Trainer「Squid also checks source and destination rules.」
- Developer「I will test successful logins and denied requests.」
The helper authenticates; Squid uses that result alongside its access rules.
Squid handles the browser exchange and passes authentication work to the appropriate helper. A successful helper response does not grant unrestricted access to any destination.
| Component | What to inspect |
|---|---|
| Kerberos helper | SPN, keytab, key version, encryption types and file permissions |
| NTLM deployment | Compatible helper and DC validation path; Winbind or other components as required |
| Squid ACLs | Authentication, source, destination, ports and rule order |
| Client | Actual proxy route, supported schemes, tickets and management policy |
Helper input protocols and options differ. Do not test one scheme’s helper with guessed tokens for another. Do not present fictional success logs as actual test results.
- 1Identify the failure and time in the actual logs used by the deployment, such as
cache.log. - 2Check that the helper exists, can run, can access required files and has the correct service name and key.
- 3Reproduce the issue with a client and distinguish authentication results from access-rule denials.
- 4Enable additional diagnostic logging only as needed, and keep credentials and tokens out of shared reports.
Avoid embedding passwords in echo commands for testing. Do not paste authentication tokens or keytab contents into chat, Issues or publicly accessible logs.
4.2.4 Do not make Basic an unconditional fallback
- Developer「Is Basic safe if the website uses HTTPS?」
- Trainer「Check the client-to-proxy connection separately.」
- Trainer「Base64 does not protect Basic credentials.」
- Developer「I will allow only necessary, protected exceptions.」
Before adding Basic, establish why the exception is needed and how its credentials travel.
Basic represents the username and password in Base64, which is not encryption. Even if the destination website uses HTTPS, authentication to an HTTP proxy can happen earlier on an unencrypted connection. That does not protect the proxy credentials.
| Condition to examine | Design response |
|---|---|
| Client lacks integrated authentication | Review alternatives, device management and the intended users |
| Basic is required | Protect the client-to-proxy connection and verify certificates and client support |
| An exception must be limited | Restrict users, devices, routes and duration; distinguish it from normal access |
| A scheme must be restricted | Use a supported control; an ACL’s name does not select an authentication scheme |
For example, naming an ACL acl negotiate_auth proxy_auth REQUIRED does not make it a Negotiate-only check. proxy_auth REQUIRED matches authenticated users; the ACL name is simply an administrator-chosen label.
When several schemes are advertised, client implementation and policy influence selection. Do not design a supposedly safe automatic sequence that always drops from Kerberos to NTLM and then to Basic on failure.
Proxy authentication provides a foundation for associating traffic with an account. Part 5 covers how clients route their traffic through that proxy.
Company-wide AI security—consult with us on everything from foundations to operations.
From foundations such as identity and access management to LLM-specific risks (prompt injection, information leaks, harmful outputs)—using AI safely in an organization involves a wide range of issues.
We develop and provide our own LLM audit product, "LLM-Audit." Drawing on that expertise, we provide practical support from audits and assessments to defensive measures and secure operational design.
See our LLM security services →